Monitor a host with ping
What it does
Section titled “What it does”A ping monitor sends ICMP echo requests to a hostname or IP address on each check interval and confirms the host responds — basic reachability, no port, no application-level check. Use it for infrastructure you want a heartbeat on without an HTTP endpoint or an open TCP port.
Set it up in the app
Section titled “Set it up in the app”- In the dashboard, click Add to create a monitor.
- Set Type to Ping.
- Enter a Name (for example
edge-router-1). - Enter the target in the Hostname field, for example
edge1.example.com— no scheme, path, or port. - Click Add.
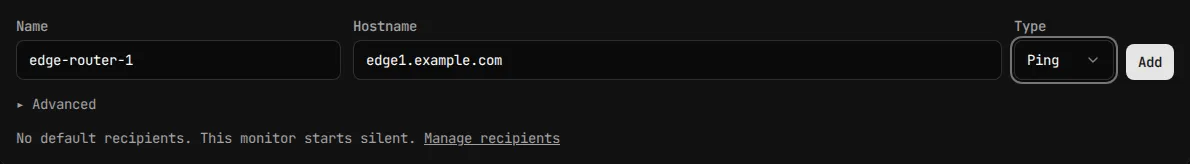
Do the same through the API or MCP
Section titled “Do the same through the API or MCP”curl -X POST https://api.uptimemonitoring.com/api/v1/monitors \ -H "Authorization: Bearer $UPTIMEMONITORING_API_KEY" \ -H "Content-Type: application/json" \ -d '{ "name": "edge-router-1", "url": "edge1.example.com", "type": "ping" }'The url field for type: "ping" is a bare hostname or IP literal — no scheme, path, or port. expected_status and body_match are ignored. As with TCP monitors, the create response returns state.status: "unknown"; the next scheduled check fills in up or down. See Monitors for the full create/update/delete reference.
Through MCP, ask your agent to create a monitor with type: ping and the bare hostname; the create_monitor tool accepts the same shape. See Use UptimeMonitoring through MCP.
Plan limits
Section titled “Plan limits”The ping target’s hostname is capped at 253 characters (pingHostMaxLen in um-api’s internal/checker/ssrf.go) — the standard DNS full-name length limit, including label-separating dots. A hostname longer than that is rejected before a check ever runs.
See Monitors for the shared monitor limits (name length, monitor count caps, 60-second minimum check interval).
Troubleshooting
Section titled “Troubleshooting”“host must be 253 characters or fewer.” Your target hostname exceeds the DNS name-length limit. Double check you haven’t pasted a URL (with a scheme or path) into the hostname field by mistake — only a bare hostname or IP literal is accepted.
The monitor shows unknown right after creation. Expected — ping monitors don’t get the immediate test check HTTP monitors do. Wait for the next scheduled check.
ICMP is blocked but the host is actually up. Some hosts and networks drop ICMP echo requests entirely (security policy, cloud provider default, etc.) even though the service behind them is healthy. If that’s the case for your target, an HTTP or TCP monitor against an actual service port is more reliable than ping.